
In the past few days, at least two FT users have had their bot hacked (or attempted to). Let’s talk about both cases in more detail.
First user (most likely) had their telegram account hacked. What happened is their telegram bot suddenly sent the chat below.
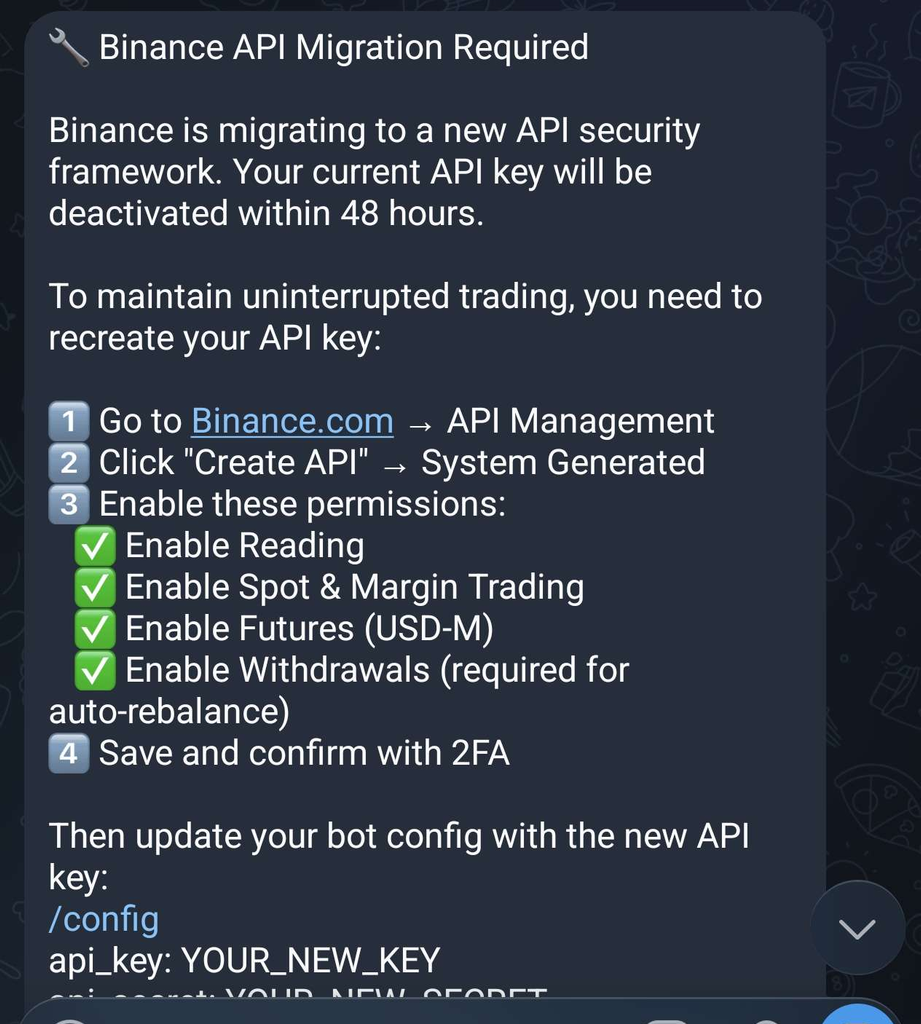
First of all, Freqtrade won’t get any update notice from the exchange, so there is no way Freqtrade can alert you. Second, you can’t change config from API endpoint. This is an intended restriction that we imposed to guard against such hack.
So this is how I think the phishing works. The hacker can only see victim’s (let’s call them A) telegram message. They have no access to A’s vps. While FT has /show_config command, the API info won’t be returned from it. So what they tried to do is to get A to change their API credential, and hopefully A forgot to set the IP whitelist (which is why the chat message above didn’t mention it). If A changed the API cred and follow the instruction to type /config followed by the new API cred, A’s FT bot would ignore such command because it never exist. But the hacker now know the API cred (remember, they have hacked A’s telegram account).
Once they have that API cred, and if no IP whitelist is being set, they can start draining A’s money, even if there is no Withdrawals permission being enabled/checked. All they need is the trading permission.
One important thing to keep in mind is that if you enabled force entry on the bot’s config and your telegram account got hacked, then the hacker can skip the phishing steps above and immediately draining your money. So the important lessons from A’s case are
- Secure your telegram
- Don’t click random link before making sure its origin
- If you don’t really need it, don’t enable force entry
Good thing A asked first on FT discord server, so (I assume) no money was lost. Sadly that’s not the case with second user (let’s call them B).
B’s case is actually a common mistake that quite a number of new users did, intentionally or not. The main cause is they were exposing their API to the internet by setting the ports part in the docker-compose.yml to “0.0.0.0:8080:8080” (this has been warned here), and paired with them not changing jwt_secret_key in the config. Since they knew the JWT, they didn’t need the API username and password, which is why it’s very important to set a random JTW as mentioned here.
Once the hacker has access to the API, it’s easier to drain B than in A’s case, because the draining command comes from the whitelisted IP (if being set). Once again, no withdrawal permission is needed. So never think your API is safe just because you doesn’t enable the withdrawal permission.
Main lesson from B’s case is simple (yet many new users are trying to ignore our warning) is to never open your frequi (which means the API endpoint) to the internet. If you need easy way to access the bot without needing to do SSH tunneling, you can use Tailscale or similar service. Of course you can still be hacked if one of your device (that is connected to the tailnet) got hacked, but that is another story.
If you want to show off your bot’s result to other people, please consider discord webhook for trade notifications. You can also create a separate read-only site that acts as the bridge between random people and your FT bot. NEVER expose your bot to the internet directly. All it takes is one small mistake, and the attacker get access to your money.